mirror of
https://github.com/block/buzz.git
synced 2026-11-05 08:51:10 +00:00
 d8281b9c93
**Category:** new-feature **User Impact:** Mobile users must confirm with Face ID, biometrics, or their device passcode before sending their Buzz identity to Desktop. **Problem:** A signed-in phone could send its full identity, including the `nsec`, to a desktop without fresh local verification. **Solution:** Require OS device authentication before opening the identity-recovery scanner, retain that authorization only for the active pairing session and short pairing window, and require fresh authentication again if it expires before the identity payload is sent. Normal app opening, identity import, and community removal remain unchanged. ## Screencasts | Enable Face ID | Use Face ID | | --- | --- | | 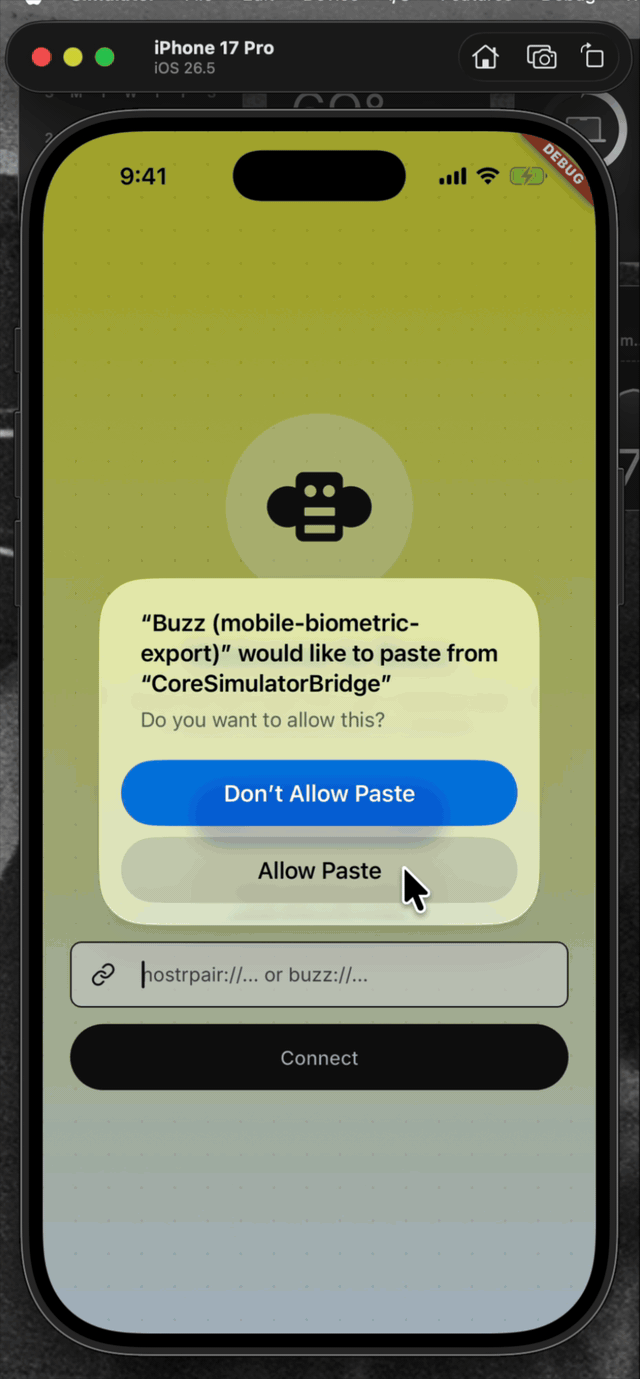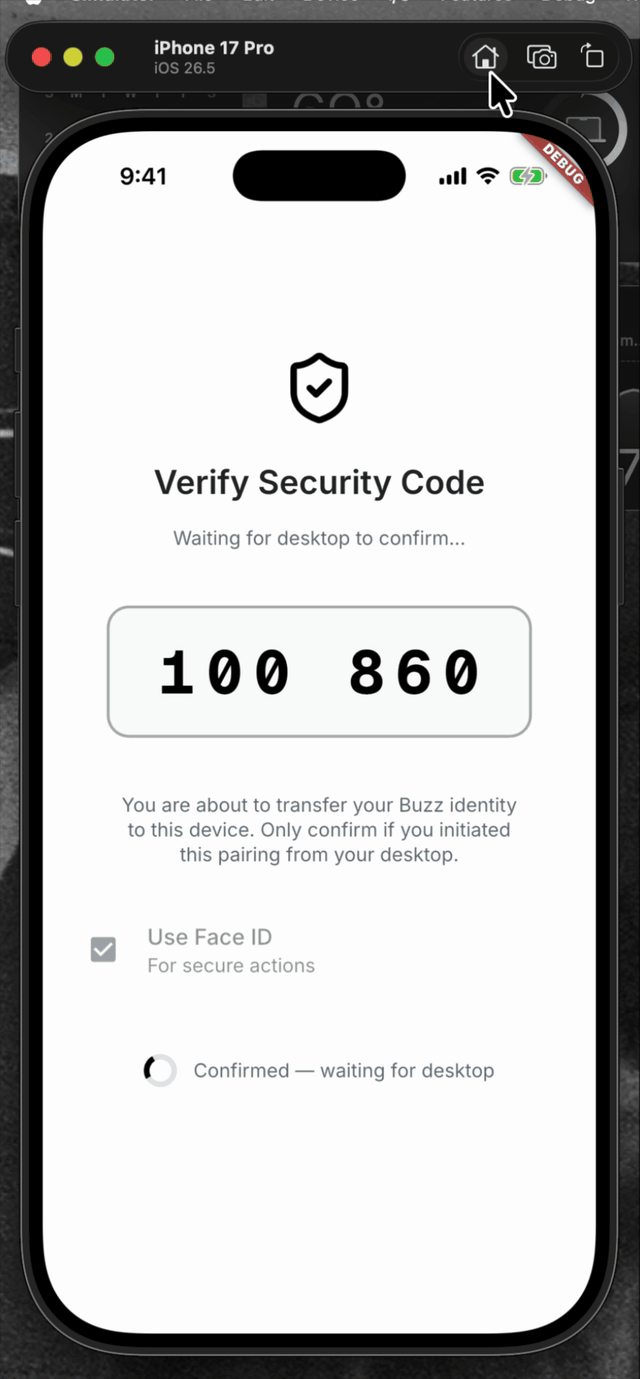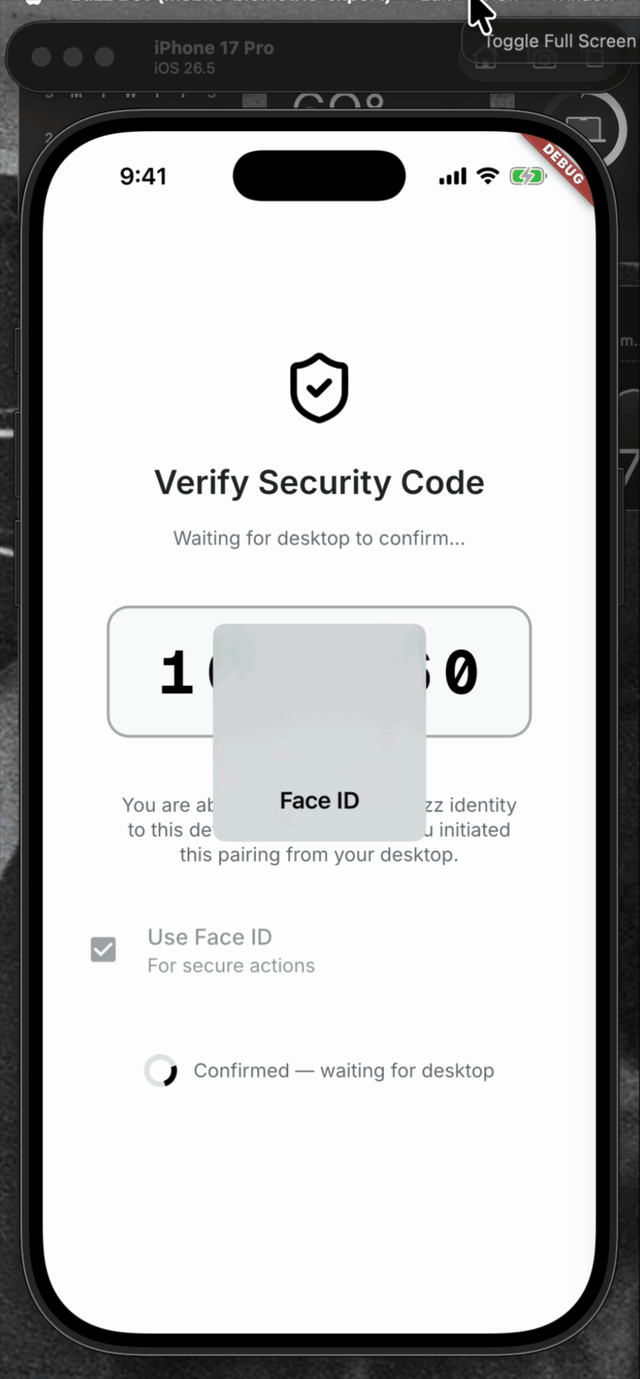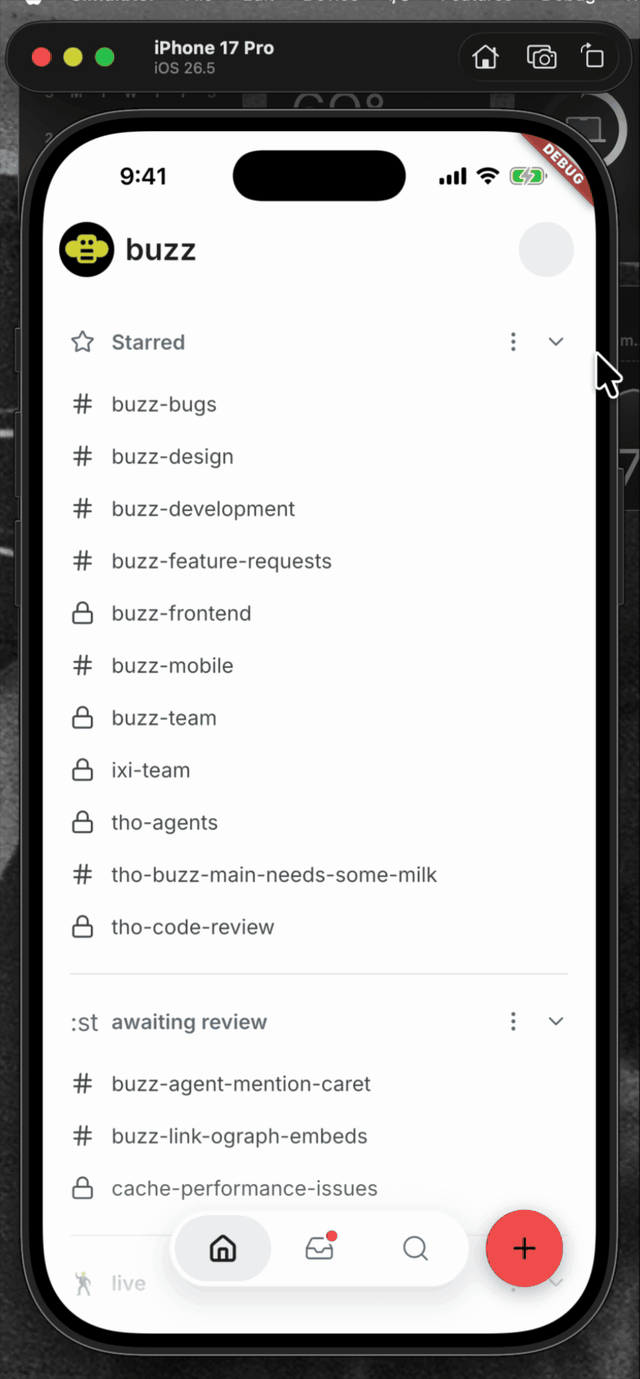 | 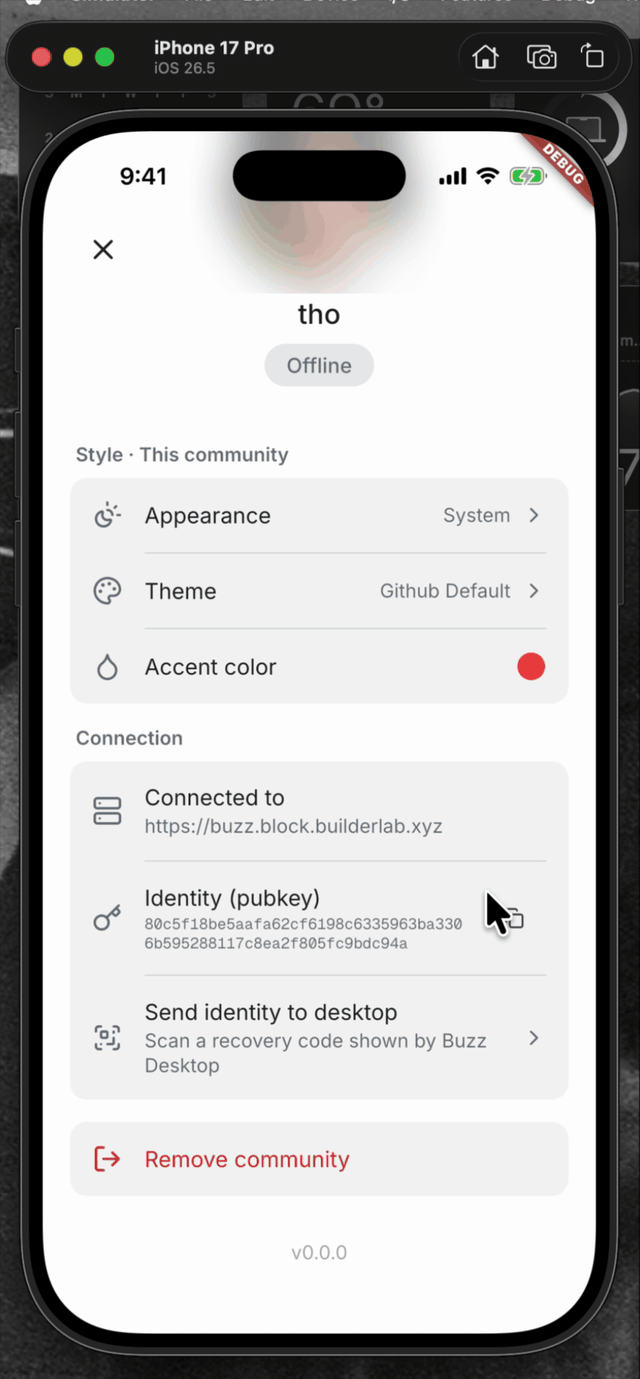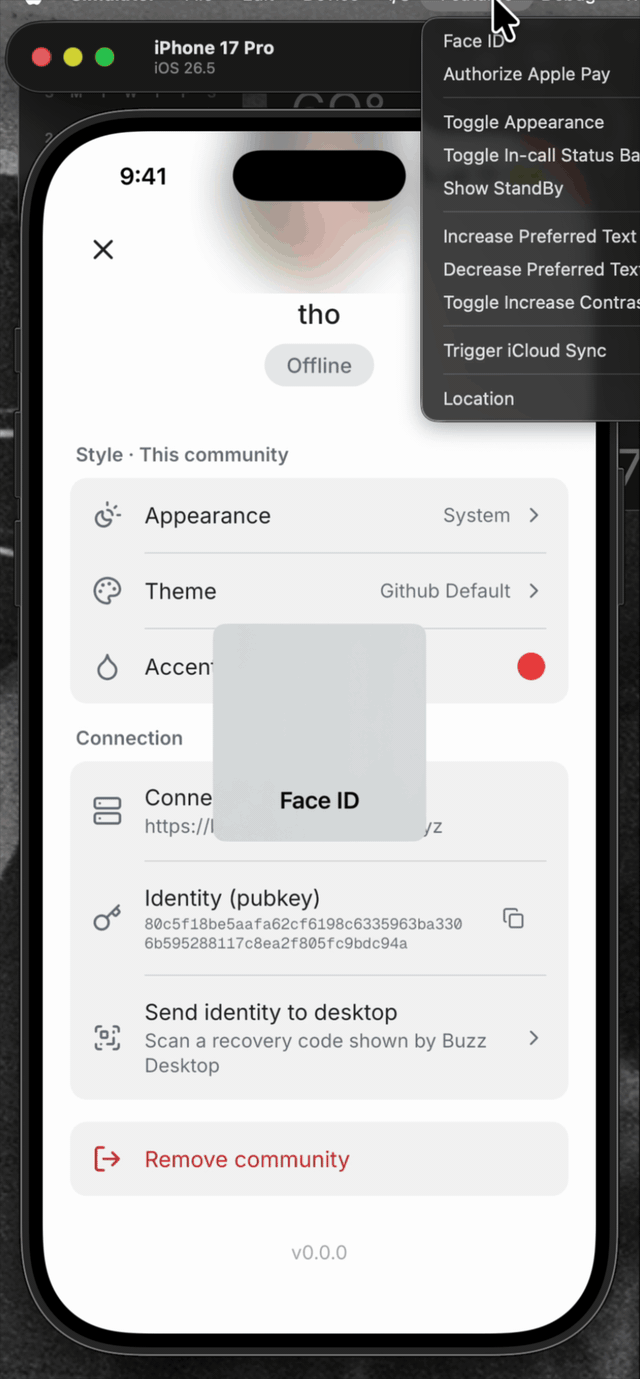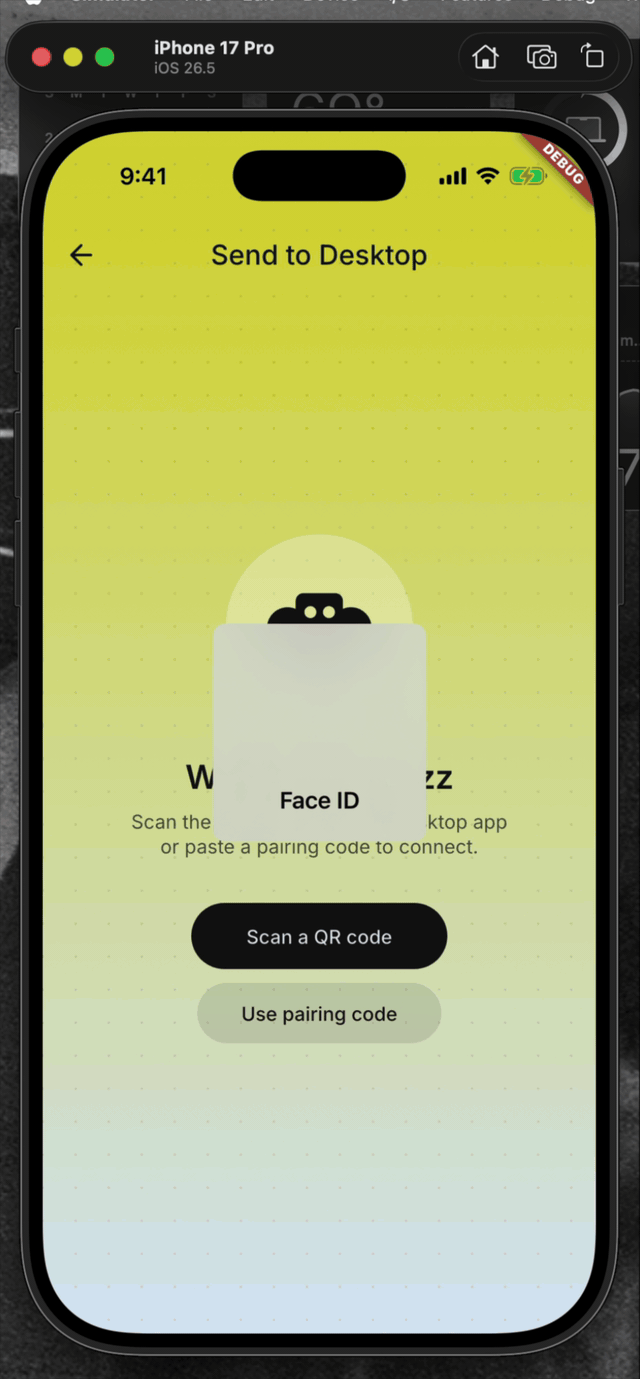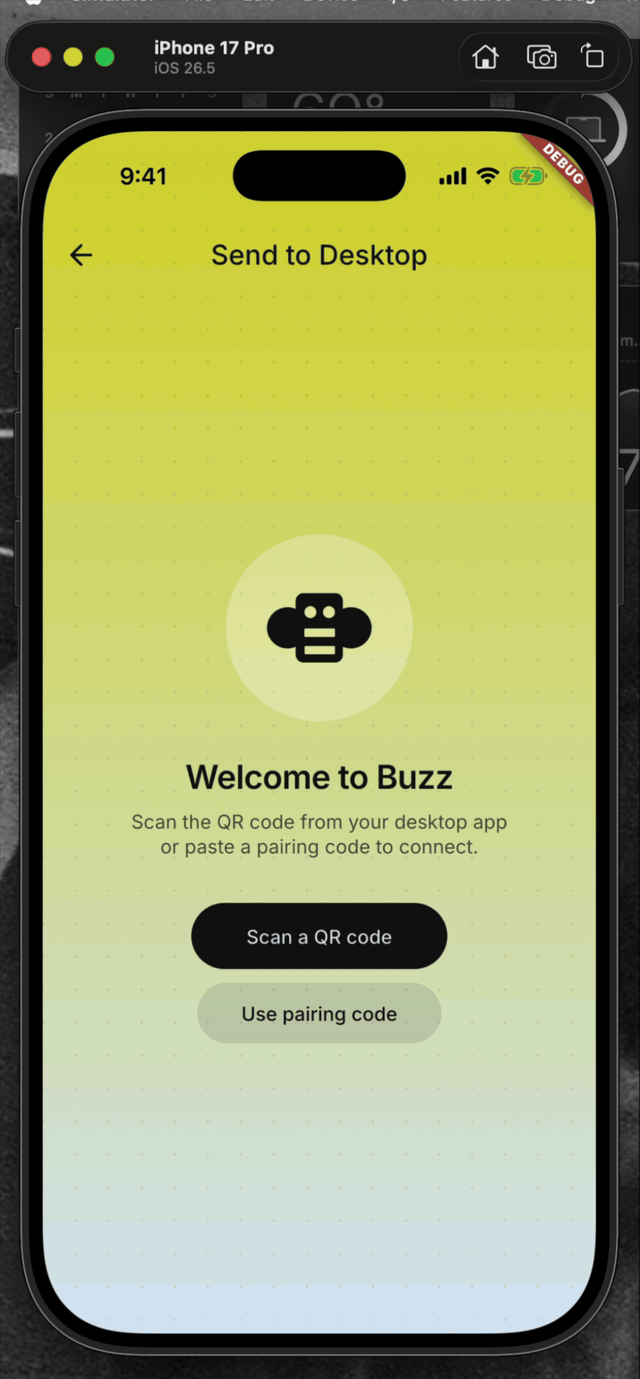 | <details> <summary>File changes</summary> **Android and iOS integration** - `mobile/android/app/build.gradle.kts` declares the AppCompat dependency required by the biometric activity theme. - `mobile/android/app/src/main/kotlin/xyz/block/buzz/mobile/MainActivity.kt` uses the activity type required by the system authentication prompt. - `mobile/android/app/src/main/res/values/styles.xml` and `mobile/android/app/src/main/res/values-night/styles.xml` use the compatible launch theme. - `mobile/ios/Podfile.lock` records the native local-authentication dependency. - `mobile/ios/Runner/Info.plist` explains why Buzz requests Face ID access. **Identity policy and pairing flow** - `mobile/lib/shared/security/sensitive_action_authorizer.dart` wraps OS authentication and maps platform errors to stable app-level outcomes. - `mobile/lib/shared/community/community.dart` and `mobile/lib/shared/community/community_storage.dart` persist the sensitive-action policy. - `mobile/lib/features/invites/invite_join_provider.dart` assigns the explicit policy for invite-created communities. - `mobile/lib/features/pairing/pairing_provider.dart` gates export, binds grants to the active community/session, reauthenticates expired grants, and clears grants on every terminal path. - `mobile/lib/features/pairing/pairing_page.dart` lets users choose biometric protection while importing an identity. - `mobile/lib/features/settings/settings_page.dart` wires pairing into settings. - `mobile/lib/features/settings/settings_page/connection_section.dart` authenticates before opening export recovery and bounds the foreground-resume wait. - `mobile/pubspec.yaml` and `mobile/pubspec.lock` add and lock `local_auth`. **Coverage** - `mobile/test/shared/security/sensitive_action_authorizer_test.dart` covers native result mapping, unsupported devices, and single-flight behavior. - `mobile/test/shared/community/community_test.dart` and `mobile/test/shared/community/community_storage_test.dart` cover policy defaults and persistence. - `mobile/test/features/invites/invite_join_provider_test.dart` covers the invite policy. - `mobile/test/features/pairing/pairing_page_test.dart` covers import protection controls. - `mobile/test/features/pairing/pairing_provider_test.dart` covers export/import authorization, stale/reset/concurrent guards, malformed payload cleanup, and no-export failure paths. - `mobile/test/features/settings/connection_section_test.dart` covers the tap gate, lifecycle resume, and timeout behavior. </details> ## Reproduction steps 1. Pair an identity into the mobile app. 2. Open Settings and choose “Send identity to desktop.” 3. Verify Face ID, biometrics, or the device passcode is required before the recovery scanner opens. 4. Cancel device authentication and verify the scanner does not open and no identity transfer begins. 5. Authenticate, scan a Desktop recovery code, confirm the SAS, and verify the identity transfer completes. ## Validation At `be5620f5f10aa6cc16e86a4f01f102f3d9aeef9b`: - `cd mobile && ../bin/flutter analyze` — no issues - `cd mobile && ../bin/flutter test` — 1,368 tests passed - `cd mobile/android && JAVA_HOME=$(/usr/libexec/java_home -v 21) ./gradlew app:assembleDebug` — debug APK assembled successfully --------- Signed-off-by: Taylor Ho <taylorkmho@gmail.com>


341 lines
11 KiB
Dart
341 lines
11 KiB
Dart
import 'dart:convert';
|
|
|
|
import 'package:flutter_test/flutter_test.dart';
|
|
import 'package:hooks_riverpod/hooks_riverpod.dart';
|
|
import 'package:http/http.dart' as http;
|
|
import 'package:http/testing.dart' as http_testing;
|
|
import 'package:nostr/nostr.dart' as nostr;
|
|
import 'package:pointycastle/digests/sha256.dart';
|
|
|
|
import 'package:buzz/features/invites/invite_join_provider.dart';
|
|
import 'package:buzz/shared/auth/auth.dart';
|
|
import 'package:buzz/shared/deeplink/deep_link.dart';
|
|
|
|
import '../../shared/community/community_storage_test.dart';
|
|
|
|
void main() {
|
|
for (final existingRelayUrl in [
|
|
'wss://relay.example.com',
|
|
'https://relay.example.com',
|
|
]) {
|
|
test(
|
|
'same-relay invite switches existing $existingRelayUrl before keygen or claim',
|
|
() async {
|
|
var generatedKeys = 0;
|
|
var claimRequests = 0;
|
|
final storage = CommunityStorage(secure: FakeSecureStorage());
|
|
final existing = Community(
|
|
id: 'existing-id',
|
|
name: 'Existing',
|
|
relayUrl: existingRelayUrl,
|
|
pubkey: 'old-pubkey',
|
|
nsec: 'old-nsec',
|
|
addedAt: DateTime.utc(2026),
|
|
);
|
|
await storage.save(existing);
|
|
final auth = _RecordingAuthNotifier();
|
|
final container = ProviderContainer(
|
|
overrides: [
|
|
communityStorageProvider.overrideWithValue(storage),
|
|
authProvider.overrideWith(() => auth),
|
|
inviteKeyGeneratorProvider.overrideWithValue(() {
|
|
generatedKeys++;
|
|
return nostr.Keys.generate();
|
|
}),
|
|
inviteJoinHttpClientProvider.overrideWithValue(
|
|
http_testing.MockClient((request) async {
|
|
claimRequests++;
|
|
return http.Response('{}', 500);
|
|
}),
|
|
),
|
|
],
|
|
);
|
|
addTearDown(container.dispose);
|
|
await container.read(communityListProvider.future);
|
|
|
|
await container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(
|
|
relayUrl: 'wss://relay.example.com',
|
|
code: 'code',
|
|
),
|
|
);
|
|
|
|
final state = container.read(inviteJoinProvider);
|
|
final stored = (await storage.loadAll()).single;
|
|
expect(state.status, InviteJoinStatus.switchedExisting);
|
|
expect(await storage.loadActiveId(), existing.id);
|
|
expect(stored.relayUrl, existingRelayUrl);
|
|
expect(stored.pubkey, 'old-pubkey');
|
|
expect(stored.nsec, 'old-nsec');
|
|
expect(generatedKeys, 0);
|
|
expect(claimRequests, 0);
|
|
expect(auth.authenticatedCommunities, isEmpty);
|
|
},
|
|
);
|
|
}
|
|
|
|
test(
|
|
'claim posts with freshly-generated key and stores joined community',
|
|
() async {
|
|
final keys = nostr.Keys.generate();
|
|
http.Request? capturedRequest;
|
|
final storage = CommunityStorage(secure: FakeSecureStorage());
|
|
final auth = _RecordingAuthNotifier();
|
|
final container = ProviderContainer(
|
|
overrides: [
|
|
communityStorageProvider.overrideWithValue(storage),
|
|
authProvider.overrideWith(() => auth),
|
|
inviteKeyGeneratorProvider.overrideWithValue(() => keys),
|
|
inviteJoinHttpClientProvider.overrideWithValue(
|
|
http_testing.MockClient((request) async {
|
|
capturedRequest = request;
|
|
return http.Response(
|
|
jsonEncode({
|
|
'status': 'joined',
|
|
'community_id': 'community-id',
|
|
'host': 'relay.example.com',
|
|
'role': 'member',
|
|
}),
|
|
200,
|
|
);
|
|
}),
|
|
),
|
|
],
|
|
);
|
|
addTearDown(container.dispose);
|
|
|
|
await container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(
|
|
relayUrl: 'wss://relay.example.com',
|
|
code: 'code',
|
|
),
|
|
);
|
|
expect(
|
|
container.read(inviteJoinProvider).status,
|
|
InviteJoinStatus.confirming,
|
|
);
|
|
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
|
|
final state = container.read(inviteJoinProvider);
|
|
expect(state.status, InviteJoinStatus.success);
|
|
expect(capturedRequest, isNotNull);
|
|
expect(
|
|
capturedRequest!.url.toString(),
|
|
'https://relay.example.com/api/invites/claim',
|
|
);
|
|
expect(capturedRequest!.body, jsonEncode({'code': 'code'}));
|
|
final authHeader = capturedRequest!.headers['Authorization'];
|
|
expect(authHeader, startsWith('Nostr '));
|
|
expect(capturedRequest!.followRedirects, isFalse);
|
|
final encoded = authHeader!.substring('Nostr '.length);
|
|
final authEvent =
|
|
jsonDecode(
|
|
utf8.decode(base64Url.decode(base64Url.normalize(encoded))),
|
|
)
|
|
as Map<String, dynamic>;
|
|
final tags = (authEvent['tags'] as List<dynamic>)
|
|
.map((tag) => (tag as List<dynamic>).cast<String>())
|
|
.toList();
|
|
final payloadHash = SHA256Digest()
|
|
.process(capturedRequest!.bodyBytes)
|
|
.map((byte) => byte.toRadixString(16).padLeft(2, '0'))
|
|
.join();
|
|
expect(authEvent['kind'], 27235);
|
|
expect(tags, contains(equals(['u', capturedRequest!.url.toString()])));
|
|
expect(tags, contains(equals(['method', 'POST'])));
|
|
expect(tags, contains(equals(['payload', payloadHash])));
|
|
expect(auth.authenticatedCommunities, hasLength(1));
|
|
expect(
|
|
auth.authenticatedCommunities.single.relayUrl,
|
|
'wss://relay.example.com',
|
|
);
|
|
expect(auth.authenticatedCommunities.single.pubkey, keys.public);
|
|
expect(auth.authenticatedCommunities.single.nsec, keys.nsec);
|
|
expect(
|
|
auth.authenticatedCommunities.single.sensitiveActionPolicy,
|
|
SensitiveActionPolicy.disabledByUser,
|
|
);
|
|
},
|
|
);
|
|
|
|
test('prepare rejects an unsafe relay before showing confirmation', () async {
|
|
final container = ProviderContainer();
|
|
addTearDown(container.dispose);
|
|
|
|
await expectLater(
|
|
container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(relayUrl: 'wss://127.0.0.1', code: 'code'),
|
|
),
|
|
throwsFormatException,
|
|
);
|
|
expect(container.read(inviteJoinProvider).status, InviteJoinStatus.idle);
|
|
});
|
|
|
|
test('join_policy_required requires a fresh link and cannot retry', () async {
|
|
final keys = nostr.Keys.generate();
|
|
var attempts = 0;
|
|
final storage = CommunityStorage(secure: FakeSecureStorage());
|
|
final container = ProviderContainer(
|
|
overrides: [
|
|
communityStorageProvider.overrideWithValue(storage),
|
|
inviteKeyGeneratorProvider.overrideWithValue(() => keys),
|
|
inviteJoinHttpClientProvider.overrideWithValue(
|
|
http_testing.MockClient((request) async {
|
|
attempts++;
|
|
return http.Response(
|
|
jsonEncode({'error': 'join_policy_required'}),
|
|
403,
|
|
);
|
|
}),
|
|
),
|
|
],
|
|
);
|
|
addTearDown(container.dispose);
|
|
|
|
await container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(
|
|
relayUrl: 'wss://relay.example.com',
|
|
code: 'code',
|
|
policyReceipt: 'expired.receipt',
|
|
),
|
|
);
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
|
|
final state = container.read(inviteJoinProvider);
|
|
expect(state.status, InviteJoinStatus.error);
|
|
expect(state.requiresFreshInvite, isTrue);
|
|
expect(
|
|
state.errorMessage,
|
|
'This invite approval has expired. Re-open the invite link to try again.',
|
|
);
|
|
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
expect(attempts, 1);
|
|
});
|
|
|
|
test('invite_exhausted requires a fresh invite and cannot retry', () async {
|
|
final keys = nostr.Keys.generate();
|
|
var attempts = 0;
|
|
final storage = CommunityStorage(secure: FakeSecureStorage());
|
|
final container = ProviderContainer(
|
|
overrides: [
|
|
communityStorageProvider.overrideWithValue(storage),
|
|
inviteKeyGeneratorProvider.overrideWithValue(() => keys),
|
|
inviteJoinHttpClientProvider.overrideWithValue(
|
|
http_testing.MockClient((request) async {
|
|
attempts++;
|
|
return http.Response(
|
|
jsonEncode({'error': 'invite_exhausted'}),
|
|
403,
|
|
);
|
|
}),
|
|
),
|
|
],
|
|
);
|
|
addTearDown(container.dispose);
|
|
|
|
await container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(
|
|
relayUrl: 'wss://relay.example.com',
|
|
code: 'v2.exhausted-secret',
|
|
),
|
|
);
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
|
|
final state = container.read(inviteJoinProvider);
|
|
expect(state.status, InviteJoinStatus.error);
|
|
expect(state.requiresFreshInvite, isTrue);
|
|
expect(
|
|
state.errorMessage,
|
|
'This invite has reached its use limit. Ask for a new invite.',
|
|
);
|
|
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
expect(attempts, 1);
|
|
});
|
|
|
|
test('failed claim can be retried and preserves policy receipt', () async {
|
|
final keys = nostr.Keys.generate();
|
|
var attempts = 0;
|
|
final bodies = <String>[];
|
|
final storage = CommunityStorage(secure: FakeSecureStorage());
|
|
final auth = _RecordingAuthNotifier();
|
|
final container = ProviderContainer(
|
|
overrides: [
|
|
communityStorageProvider.overrideWithValue(storage),
|
|
authProvider.overrideWith(() => auth),
|
|
inviteKeyGeneratorProvider.overrideWithValue(() => keys),
|
|
inviteJoinHttpClientProvider.overrideWithValue(
|
|
http_testing.MockClient((request) async {
|
|
attempts++;
|
|
bodies.add(request.body);
|
|
if (attempts == 1) {
|
|
return http.Response(jsonEncode({'error': 'temporary'}), 503);
|
|
}
|
|
return http.Response(
|
|
jsonEncode({
|
|
'status': 'joined',
|
|
'host': 'relay.example.com',
|
|
'role': 'member',
|
|
}),
|
|
200,
|
|
);
|
|
}),
|
|
),
|
|
],
|
|
);
|
|
addTearDown(container.dispose);
|
|
|
|
await container
|
|
.read(inviteJoinProvider.notifier)
|
|
.prepare(
|
|
const InviteDeepLink(
|
|
relayUrl: 'wss://relay.example.com',
|
|
code: 'code',
|
|
policyReceipt: 'receipt.value',
|
|
),
|
|
);
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
expect(container.read(inviteJoinProvider).status, InviteJoinStatus.error);
|
|
|
|
await container.read(inviteJoinProvider.notifier).confirmJoin();
|
|
|
|
expect(container.read(inviteJoinProvider).status, InviteJoinStatus.success);
|
|
expect(attempts, 2);
|
|
expect(
|
|
bodies,
|
|
everyElement(
|
|
jsonEncode({'code': 'code', 'policy_receipt': 'receipt.value'}),
|
|
),
|
|
);
|
|
expect(auth.authenticatedCommunities, hasLength(1));
|
|
});
|
|
}
|
|
|
|
class _RecordingAuthNotifier extends AuthNotifier {
|
|
final List<Community> authenticatedCommunities = [];
|
|
|
|
@override
|
|
Future<AuthState> build() async =>
|
|
const AuthState(status: AuthStatus.unauthenticated);
|
|
|
|
@override
|
|
Future<void> authenticateWithCommunity(Community community) async {
|
|
authenticatedCommunities.add(community);
|
|
state = AsyncData(
|
|
AuthState(status: AuthStatus.authenticated, community: community),
|
|
);
|
|
}
|
|
}
|