mirror of
https://github.com/block/buzz.git
synced 2026-10-30 14:01:37 +00:00
 d8281b9c93
**Category:** new-feature **User Impact:** Mobile users must confirm with Face ID, biometrics, or their device passcode before sending their Buzz identity to Desktop. **Problem:** A signed-in phone could send its full identity, including the `nsec`, to a desktop without fresh local verification. **Solution:** Require OS device authentication before opening the identity-recovery scanner, retain that authorization only for the active pairing session and short pairing window, and require fresh authentication again if it expires before the identity payload is sent. Normal app opening, identity import, and community removal remain unchanged. ## Screencasts | Enable Face ID | Use Face ID | | --- | --- | | 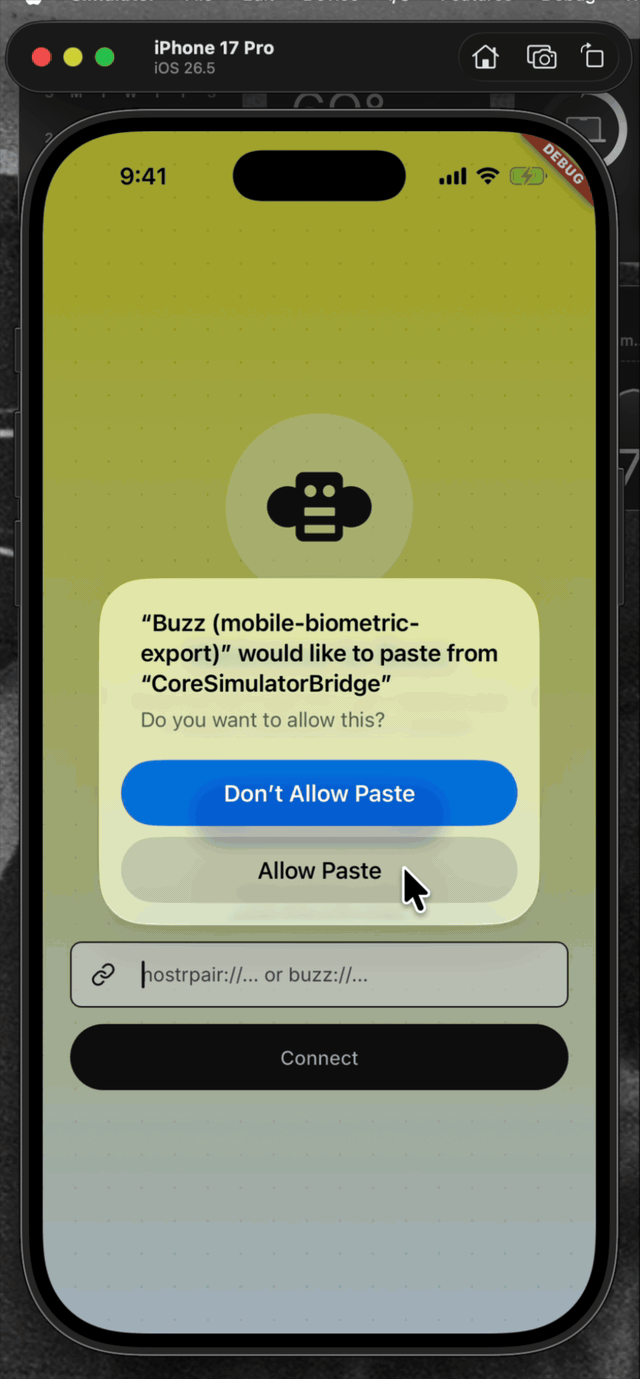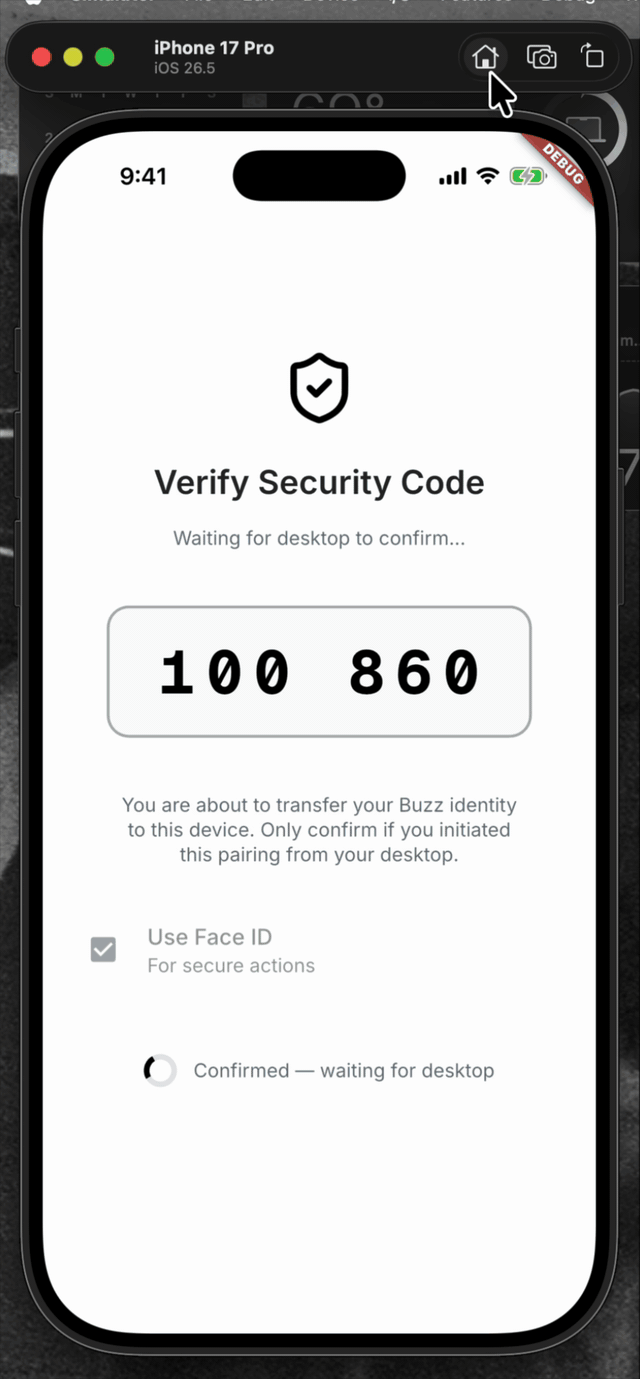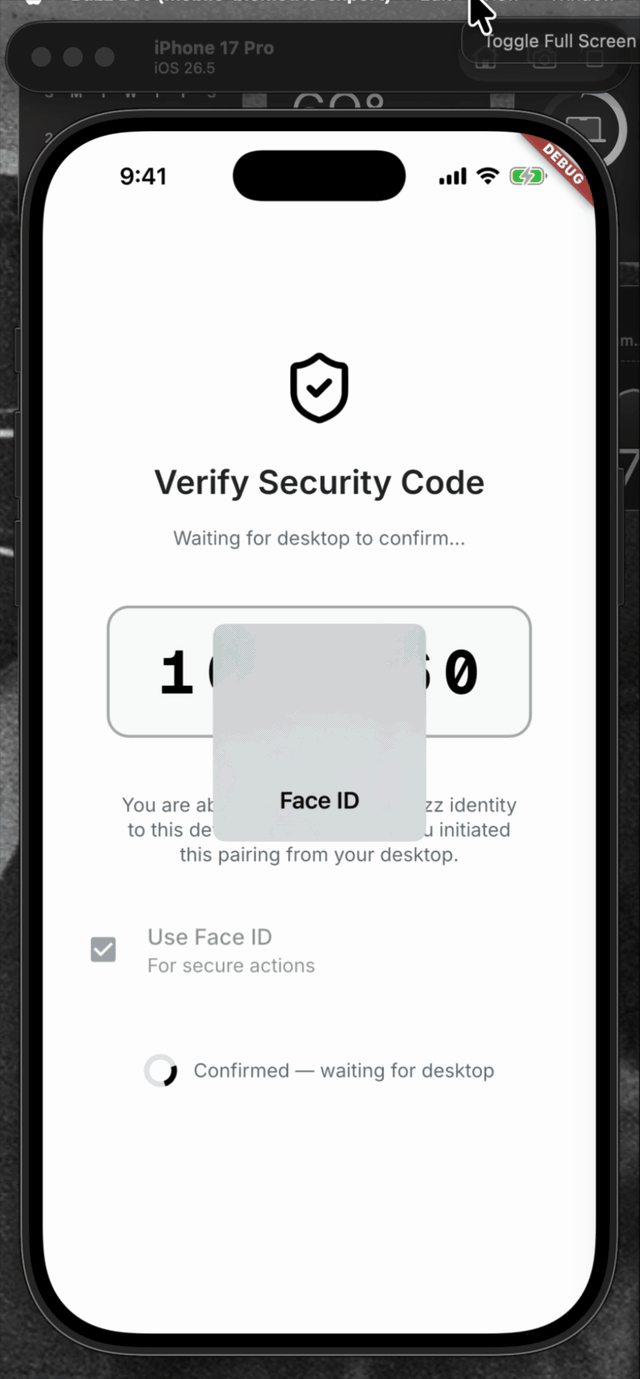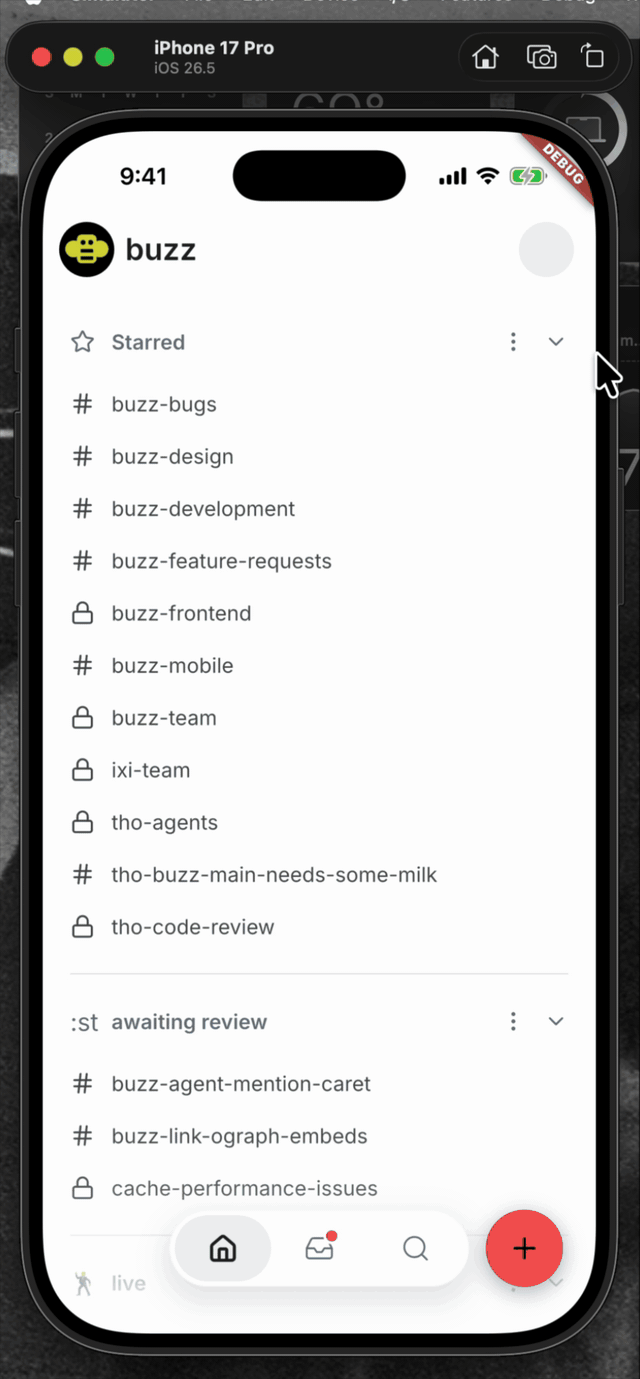 | 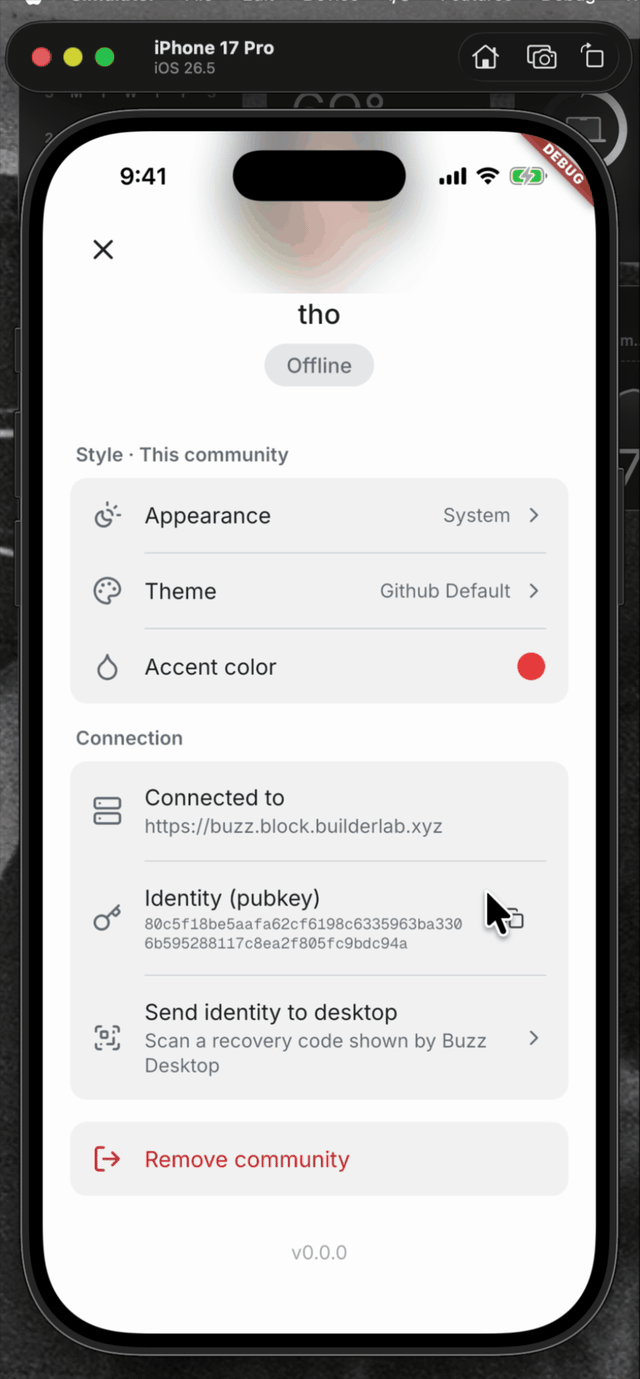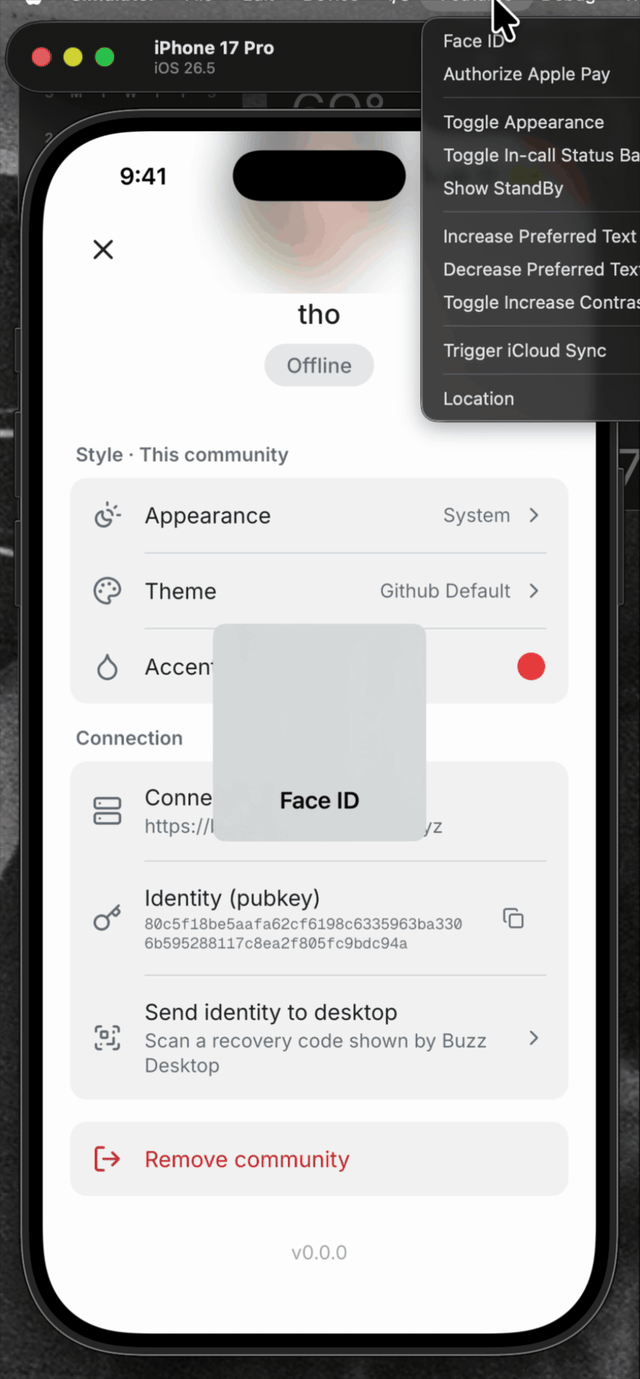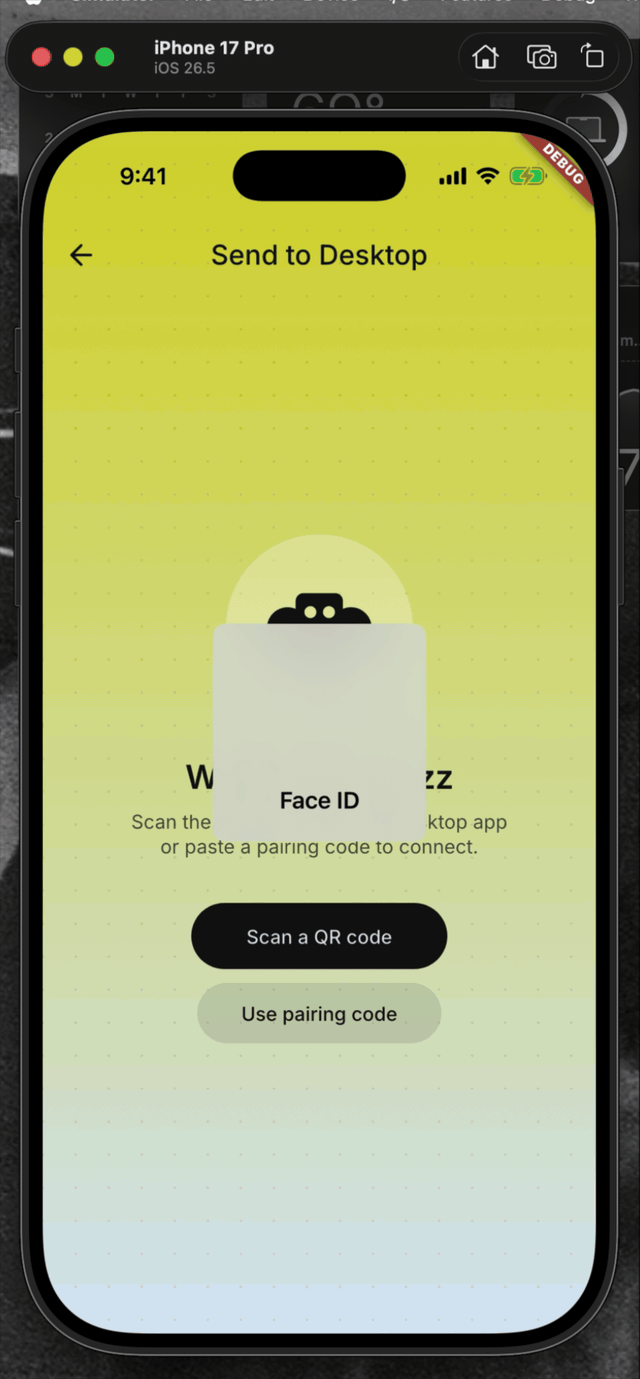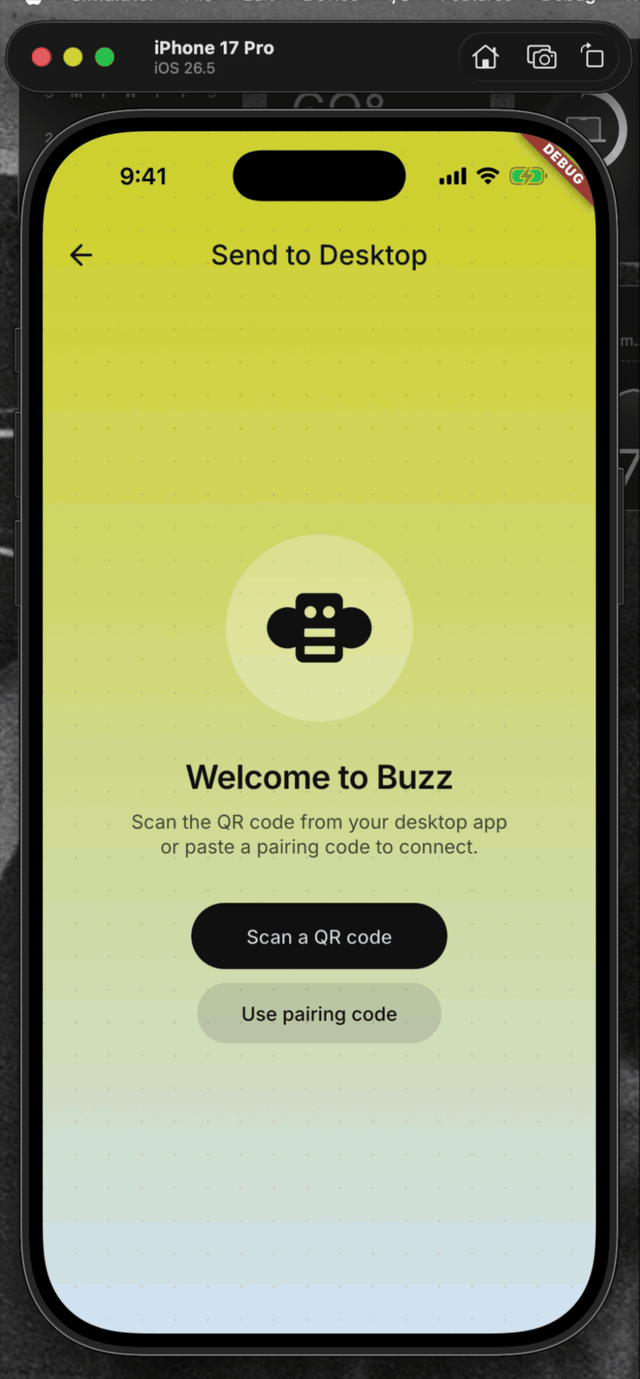 | <details> <summary>File changes</summary> **Android and iOS integration** - `mobile/android/app/build.gradle.kts` declares the AppCompat dependency required by the biometric activity theme. - `mobile/android/app/src/main/kotlin/xyz/block/buzz/mobile/MainActivity.kt` uses the activity type required by the system authentication prompt. - `mobile/android/app/src/main/res/values/styles.xml` and `mobile/android/app/src/main/res/values-night/styles.xml` use the compatible launch theme. - `mobile/ios/Podfile.lock` records the native local-authentication dependency. - `mobile/ios/Runner/Info.plist` explains why Buzz requests Face ID access. **Identity policy and pairing flow** - `mobile/lib/shared/security/sensitive_action_authorizer.dart` wraps OS authentication and maps platform errors to stable app-level outcomes. - `mobile/lib/shared/community/community.dart` and `mobile/lib/shared/community/community_storage.dart` persist the sensitive-action policy. - `mobile/lib/features/invites/invite_join_provider.dart` assigns the explicit policy for invite-created communities. - `mobile/lib/features/pairing/pairing_provider.dart` gates export, binds grants to the active community/session, reauthenticates expired grants, and clears grants on every terminal path. - `mobile/lib/features/pairing/pairing_page.dart` lets users choose biometric protection while importing an identity. - `mobile/lib/features/settings/settings_page.dart` wires pairing into settings. - `mobile/lib/features/settings/settings_page/connection_section.dart` authenticates before opening export recovery and bounds the foreground-resume wait. - `mobile/pubspec.yaml` and `mobile/pubspec.lock` add and lock `local_auth`. **Coverage** - `mobile/test/shared/security/sensitive_action_authorizer_test.dart` covers native result mapping, unsupported devices, and single-flight behavior. - `mobile/test/shared/community/community_test.dart` and `mobile/test/shared/community/community_storage_test.dart` cover policy defaults and persistence. - `mobile/test/features/invites/invite_join_provider_test.dart` covers the invite policy. - `mobile/test/features/pairing/pairing_page_test.dart` covers import protection controls. - `mobile/test/features/pairing/pairing_provider_test.dart` covers export/import authorization, stale/reset/concurrent guards, malformed payload cleanup, and no-export failure paths. - `mobile/test/features/settings/connection_section_test.dart` covers the tap gate, lifecycle resume, and timeout behavior. </details> ## Reproduction steps 1. Pair an identity into the mobile app. 2. Open Settings and choose “Send identity to desktop.” 3. Verify Face ID, biometrics, or the device passcode is required before the recovery scanner opens. 4. Cancel device authentication and verify the scanner does not open and no identity transfer begins. 5. Authenticate, scan a Desktop recovery code, confirm the SAS, and verify the identity transfer completes. ## Validation At `be5620f5f10aa6cc16e86a4f01f102f3d9aeef9b`: - `cd mobile && ../bin/flutter analyze` — no issues - `cd mobile && ../bin/flutter test` — 1,368 tests passed - `cd mobile/android && JAVA_HOME=$(/usr/libexec/java_home -v 21) ./gradlew app:assembleDebug` — debug APK assembled successfully --------- Signed-off-by: Taylor Ho <taylorkmho@gmail.com>


198 lines
7.1 KiB
Dart
198 lines
7.1 KiB
Dart
import 'dart:async';
|
|
|
|
import 'package:flutter_test/flutter_test.dart';
|
|
import 'package:local_auth/local_auth.dart';
|
|
import 'package:mocktail/mocktail.dart';
|
|
import 'package:buzz/shared/security/sensitive_action_authorizer.dart';
|
|
|
|
class _MockLocalAuthentication extends Mock implements LocalAuthentication {}
|
|
|
|
void main() {
|
|
late _MockLocalAuthentication authentication;
|
|
|
|
setUp(() {
|
|
authentication = _MockLocalAuthentication();
|
|
when(authentication.isDeviceSupported).thenAnswer((_) async => true);
|
|
when(
|
|
authentication.getAvailableBiometrics,
|
|
).thenAnswer((_) async => <BiometricType>[BiometricType.face]);
|
|
when(
|
|
() => authentication.authenticate(
|
|
localizedReason: any(named: 'localizedReason'),
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: any(named: 'biometricOnly'),
|
|
sensitiveTransaction: any(named: 'sensitiveTransaction'),
|
|
persistAcrossBackgrounding: any(named: 'persistAcrossBackgrounding'),
|
|
),
|
|
).thenAnswer((_) async => true);
|
|
});
|
|
|
|
test('identity authorization retries after system backgrounding', () async {
|
|
final result = await LocalSensitiveActionAuthorizer(
|
|
authentication,
|
|
).authorizeIdentityAction(biometricOnly: false);
|
|
|
|
expect(result, DeviceAuthResult.success);
|
|
verify(
|
|
() => authentication.authenticate(
|
|
localizedReason: 'Confirm sending your Buzz identity to desktop',
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: false,
|
|
sensitiveTransaction: true,
|
|
persistAcrossBackgrounding: true,
|
|
),
|
|
).called(1);
|
|
});
|
|
|
|
test('unsupported devices fail closed before authentication', () async {
|
|
when(authentication.isDeviceSupported).thenAnswer((_) async => false);
|
|
|
|
final result = await LocalSensitiveActionAuthorizer(
|
|
authentication,
|
|
).authorizeIdentityAction(biometricOnly: false);
|
|
|
|
expect(result, DeviceAuthResult.unavailable);
|
|
verifyNever(
|
|
() => authentication.authenticate(
|
|
localizedReason: any(named: 'localizedReason'),
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: any(named: 'biometricOnly'),
|
|
sensitiveTransaction: any(named: 'sensitiveTransaction'),
|
|
persistAcrossBackgrounding: any(named: 'persistAcrossBackgrounding'),
|
|
),
|
|
);
|
|
});
|
|
|
|
const mappedExceptions = <LocalAuthExceptionCode, DeviceAuthResult>{
|
|
LocalAuthExceptionCode.userCanceled: DeviceAuthResult.cancelled,
|
|
LocalAuthExceptionCode.systemCanceled: DeviceAuthResult.cancelled,
|
|
LocalAuthExceptionCode.timeout: DeviceAuthResult.cancelled,
|
|
LocalAuthExceptionCode.temporaryLockout: DeviceAuthResult.lockedOut,
|
|
LocalAuthExceptionCode.biometricLockout: DeviceAuthResult.lockedOut,
|
|
LocalAuthExceptionCode.noCredentialsSet: DeviceAuthResult.unavailable,
|
|
LocalAuthExceptionCode.noBiometricsEnrolled: DeviceAuthResult.unavailable,
|
|
LocalAuthExceptionCode.noBiometricHardware: DeviceAuthResult.unavailable,
|
|
LocalAuthExceptionCode.biometricHardwareTemporarilyUnavailable:
|
|
DeviceAuthResult.unavailable,
|
|
LocalAuthExceptionCode.uiUnavailable: DeviceAuthResult.unavailable,
|
|
LocalAuthExceptionCode.authInProgress: DeviceAuthResult.failed,
|
|
};
|
|
for (final MapEntry(key: code, value: expected) in mappedExceptions.entries) {
|
|
test('maps ${code.name} to ${expected.name}', () async {
|
|
when(
|
|
() => authentication.authenticate(
|
|
localizedReason: any(named: 'localizedReason'),
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: any(named: 'biometricOnly'),
|
|
sensitiveTransaction: any(named: 'sensitiveTransaction'),
|
|
persistAcrossBackgrounding: any(named: 'persistAcrossBackgrounding'),
|
|
),
|
|
).thenThrow(LocalAuthException(code: code));
|
|
|
|
final result = await LocalSensitiveActionAuthorizer(
|
|
authentication,
|
|
).authorizeIdentityAction(biometricOnly: false);
|
|
|
|
expect(result, expected);
|
|
});
|
|
}
|
|
|
|
test('biometric protection requires an enrolled biometric', () async {
|
|
when(
|
|
authentication.getAvailableBiometrics,
|
|
).thenAnswer((_) async => <BiometricType>[]);
|
|
|
|
final result = await LocalSensitiveActionAuthorizer(
|
|
authentication,
|
|
).authorizeBiometricProtection();
|
|
|
|
expect(result, DeviceAuthResult.unavailable);
|
|
verifyNever(
|
|
() => authentication.authenticate(
|
|
localizedReason: any(named: 'localizedReason'),
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: any(named: 'biometricOnly'),
|
|
sensitiveTransaction: any(named: 'sensitiveTransaction'),
|
|
persistAcrossBackgrounding: any(named: 'persistAcrossBackgrounding'),
|
|
),
|
|
);
|
|
});
|
|
|
|
test(
|
|
'biometric protection does not fall back to a device passcode',
|
|
() async {
|
|
final result = await LocalSensitiveActionAuthorizer(
|
|
authentication,
|
|
).authorizeBiometricProtection();
|
|
|
|
expect(result, DeviceAuthResult.success);
|
|
verify(
|
|
() => authentication.authenticate(
|
|
localizedReason: 'Enable biometrics for secure actions',
|
|
authMessages: any(named: 'authMessages'),
|
|
biometricOnly: true,
|
|
sensitiveTransaction: true,
|
|
persistAcrossBackgrounding: true,
|
|
),
|
|
).called(1);
|
|
},
|
|
);
|
|
|
|
test('single-flight shares authorization with the same mode', () async {
|
|
final authorizer = _ControllableAuthorizer();
|
|
final session = SensitiveActionAuthorizationSession(authorizer);
|
|
|
|
final first = session.authorize(biometricOnly: false);
|
|
final second = session.authorize(biometricOnly: false);
|
|
|
|
expect(authorizer.biometricOnlyCalls, [false]);
|
|
authorizer.completeNext(DeviceAuthResult.success);
|
|
expect(await first, DeviceAuthResult.success);
|
|
expect(await second, DeviceAuthResult.success);
|
|
});
|
|
|
|
test('single-flight does not reuse a weaker in-flight mode', () async {
|
|
final authorizer = _ControllableAuthorizer();
|
|
final session = SensitiveActionAuthorizationSession(authorizer);
|
|
|
|
final passcodeAllowed = session.authorize(biometricOnly: false);
|
|
final biometricOnly = session.authorize(biometricOnly: true);
|
|
|
|
expect(authorizer.biometricOnlyCalls, [false]);
|
|
authorizer.completeNext(DeviceAuthResult.success);
|
|
expect(await passcodeAllowed, DeviceAuthResult.success);
|
|
await Future<void>.delayed(Duration.zero);
|
|
expect(authorizer.biometricOnlyCalls, [false, true]);
|
|
|
|
authorizer.completeNext(DeviceAuthResult.success);
|
|
expect(await biometricOnly, DeviceAuthResult.success);
|
|
});
|
|
}
|
|
|
|
class _ControllableAuthorizer implements SensitiveActionAuthorizer {
|
|
final biometricOnlyCalls = <bool>[];
|
|
final _pending = <Completer<DeviceAuthResult>>[];
|
|
|
|
void completeNext(DeviceAuthResult result) {
|
|
_pending.removeAt(0).complete(result);
|
|
}
|
|
|
|
@override
|
|
Future<DeviceAuthResult> authorizeIdentityAction({
|
|
required bool biometricOnly,
|
|
}) {
|
|
biometricOnlyCalls.add(biometricOnly);
|
|
final completer = Completer<DeviceAuthResult>();
|
|
_pending.add(completer);
|
|
return completer.future;
|
|
}
|
|
|
|
@override
|
|
Future<DeviceAuthResult> authorizeBiometricProtection() =>
|
|
throw UnimplementedError();
|
|
|
|
@override
|
|
Future<List<BiometricType>> enrolledBiometrics() =>
|
|
throw UnimplementedError();
|
|
}
|